A customer-reported bug needs to ship as a hotfix
The fix is small, but no single durable trail connects the complaint, the code change, the test result and the emergency approval.
The work already crosses these systems:
From scattered checks to one governed run.
Today
Support copies the case into Jira, an engineer hunts for the spec in Confluence, patches the code, chases CI, then files a ServiceNow emergency change from memory.
With NopsAI
One governed run gathers case, ticket and spec context through approved tools, reasons under the emergency-change policy the release team wrote, runs fix, test and build in an isolated container, pauses at the approval gate the pipeline declares, and attaches full run evidence to the emergency change.
It does not just automate the fix. It makes the whole emergency path repeatable and auditable.
The run, step by step.
Deterministic work first, reasoning inside the tools and written policies the pipeline bound to it, and a named human at every gate its author placed.
Trigger
A support escalation or a labelled Jira issue starts the run through an approved webhook source.
Collect context
Case history, ticket detail and the linked specification are read through read-only MCP profiles.
Verify state
Deterministic steps confirm the affected version, branch protection state and current release train.
Reason
An agent role summarizes the defect, the proposed patch surface and the regression risk, bounded by policy/platform/emergency-change — which rules out shipping a hotfix that carries a schema change.
Approve
The pipeline declares a release-owner gate here, so the run pauses for a named reviewer; self-approval is disabled for the production scope.
Execute and record
Build and test run in an isolated container; the change record links back to the run evidence.
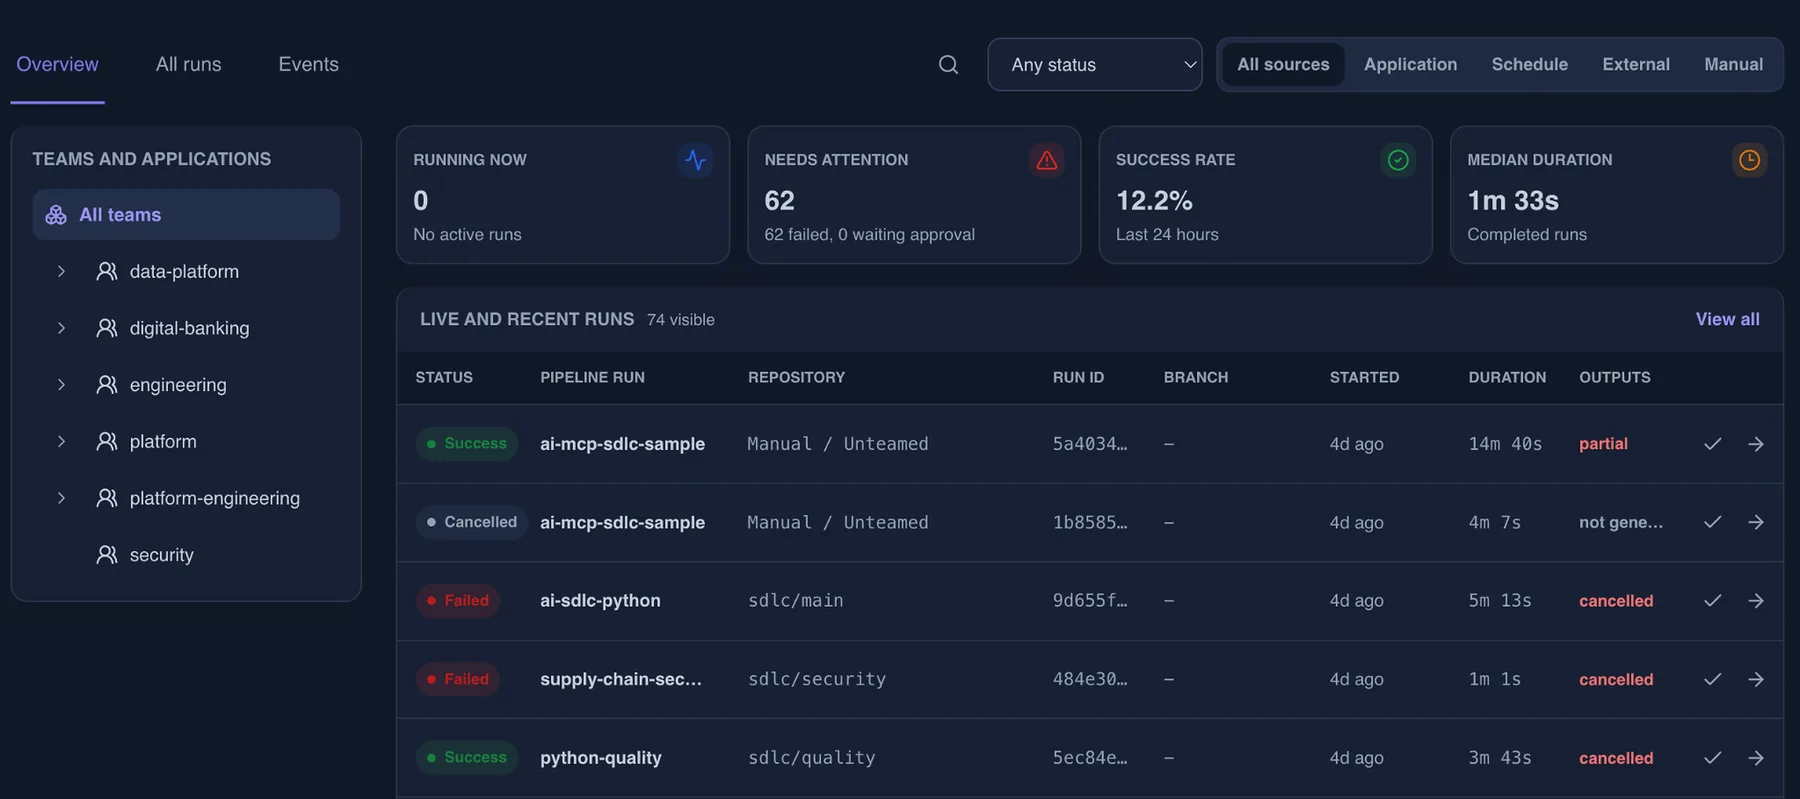
What the run leaves behind.
The useful part is not only the automation. It is repeatability with proof.
Trigger and subject
What started the run and which effective identity it ran as.
Authorization snapshot
Which resources were checked, and which decision each check returned.
Knowledge in scope
The guardrails, policies and runbooks that bounded each decision, stored as text with the run, plus the governance level that applied.
Tool and AI activity
Every tool call, the profile that allowed it, and the model usage it consumed.
Task history and timings
Every task, its state transitions, its duration and the logs it produced, with known secret values masked.
Approvals and outputs
Who approved, when, and the deliverables the run produced.
← Monthly status report to leadership
The report takes hours, invites copy-paste mistakes, and is often stale by the time leadership reads it.
Sprint planning for the next two weeks →
Planning starts with manual research instead of decisions. Blockers surface late and half-ready stories enter the sprint.
Map this workflow against your controls.
Bring the trigger, the tools it touches, the approvers, the runtime boundary and the evidence you need to keep.