QA is blocked on unclear requirements
QA loses time reconstructing intent. Testing can start from the wrong assumption and clarification cycles cost a day or more.
The work already crosses these systems:
From scattered checks to one governed run.
Today
A tester reads the ticket, hunts for the linked spec, skims the pull request, then waits for the product manager to answer in a thread.
With NopsAI
A QA-readiness pipeline pulls the ticket, linked spec and PR context, then an AI goal step drafts acceptance criteria, mismatches and questions for the PM.
Ambiguous requirements become a structured, reviewable brief before testing goes sideways.
The run, step by step.
Deterministic work first, reasoning inside the tools and written policies the pipeline bound to it, and a named human at every gate its author placed.
Trigger
A tester starts the run manually from the ticket, or a label change fires it automatically.
Collect context
Ticket, linked specification and pull-request diff are read through a read-only GitHub profile.
Verify state
Deterministic checks confirm the PR targets the expected branch and the spec version is current.
Reason
An AI goal drafts acceptance criteria and lists every mismatch between spec, ticket and code, following guideline/qa/acceptance-criteria so every brief comes back in the shape the team already reviews.
Approve
The product manager reviews the questions before they reach the team channel.
Execute and record
The brief is attached to the run and shared with sharing controls intact.
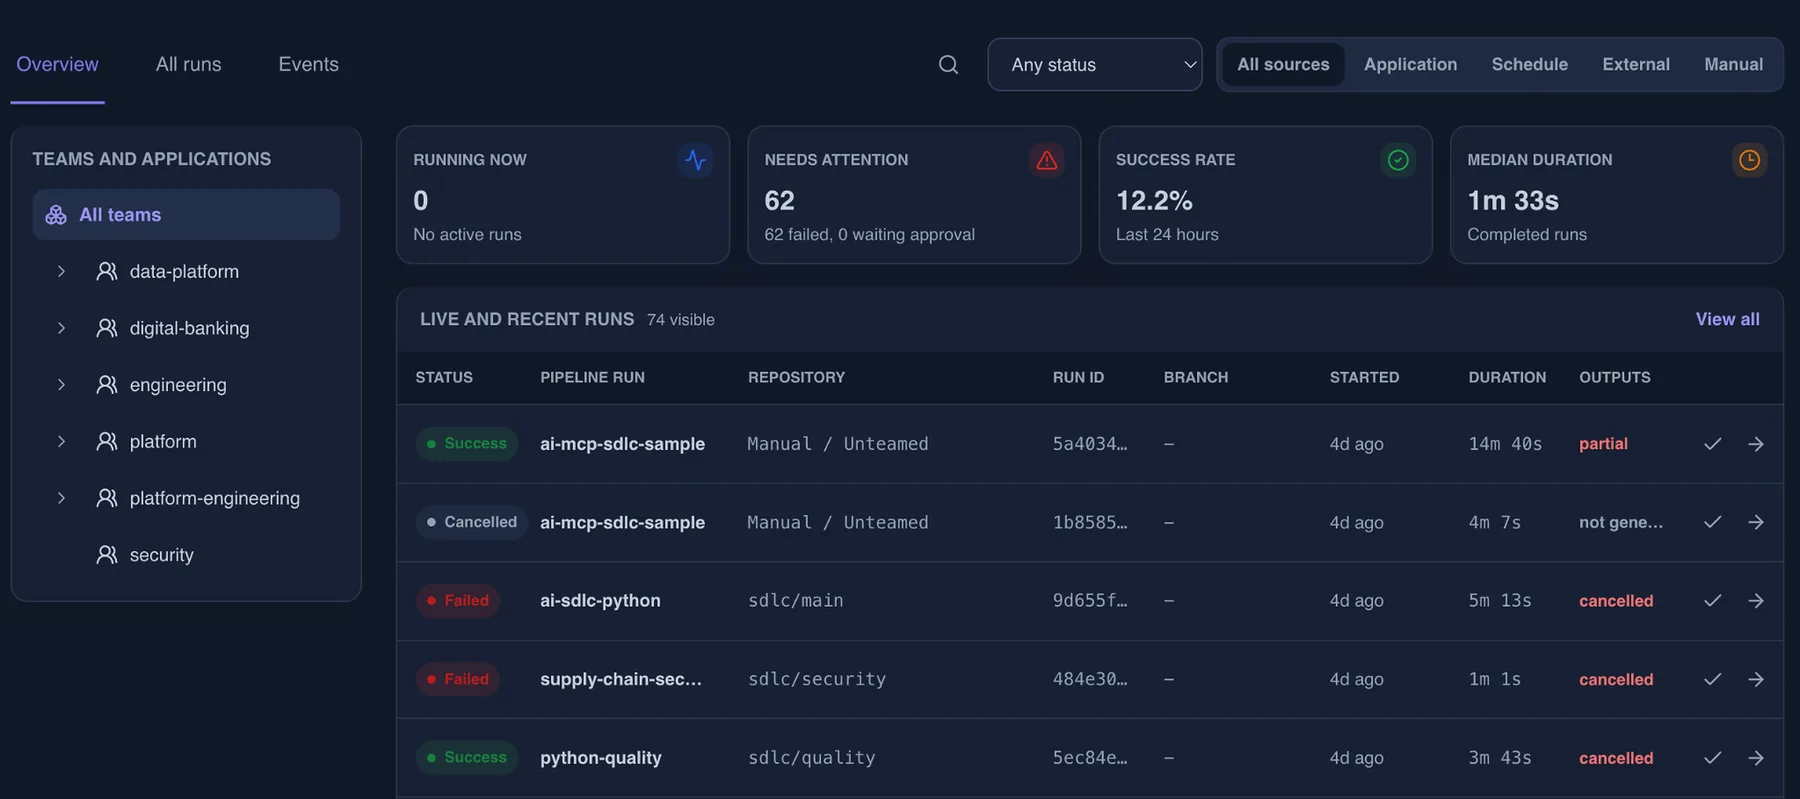
What the run leaves behind.
The useful part is not only the automation. It is repeatability with proof.
Trigger and subject
What started the run and which effective identity it ran as.
Authorization snapshot
Which resources were checked, and which decision each check returned.
Knowledge in scope
The guardrails, policies and runbooks that bounded each decision, stored as text with the run, plus the governance level that applied.
Tool and AI activity
Every tool call, the profile that allowed it, and the model usage it consumed.
Task history and timings
Every task, its state transitions, its duration and the logs it produced, with known secret values masked.
Approvals and outputs
Who approved, when, and the deliverables the run produced.
Map this workflow against your controls.
Bring the trigger, the tools it touches, the approvers, the runtime boundary and the evidence you need to keep.